You are viewing a plain text version of this content. The canonical link for it is here.
Posted to commits@magpie.apache.org by po...@apache.org on 2026/07/05 22:21:42 UTC
(magpie) branch main updated: docs: add Magpie badge asset (#758)
This is an automated email from the ASF dual-hosted git repository.
potiuk pushed a commit to branch main
in repository https://gitbox.apache.org/repos/asf/magpie.git
The following commit(s) were added to refs/heads/main by this push:
new 86a6d88e docs: add Magpie badge asset (#758)
86a6d88e is described below
commit 86a6d88ee0f58bc6e51bf30f42731d2d08ef7ab1
Author: Bartosz Sławecki <ba...@slawecki.dev>
AuthorDate: Mon Jul 6 00:21:37 2026 +0200
docs: add Magpie badge asset (#758)
* docs: add Magpie badge asset
Generated-by: GPT-5.5 via OpenCode
* Fix readme badge link
---
README.md | 2 ++
assets/badge.json | 8 ++++++++
{images => assets}/sandbox-blocks-read.png | Bin
{images => assets}/sandbox-bypass-banner.png | Bin
{images => assets}/sandbox-os-level-block.png | Bin
{images => assets}/session-no-sandbox.png | Bin
{images => assets}/session-sandboxed.png | Bin
docs/rfcs/RFC-AI-0002.md | 14 +++++++-------
docs/setup/secure-agent-setup.md | 10 +++++-----
9 files changed, 22 insertions(+), 12 deletions(-)
diff --git a/README.md b/README.md
index 8802355e..7a0a2bd0 100644
--- a/README.md
+++ b/README.md
@@ -21,6 +21,8 @@
# Apache Magpie
+[](https://magpie.apache.org/)
+
A reusable, project-agnostic framework for ASF-project automation.
Currently in development for ASF projects + Python Core team
friendlies. **Not** a public marketplace skill — adoption is by
diff --git a/assets/badge.json b/assets/badge.json
new file mode 100644
index 00000000..78a59c21
--- /dev/null
+++ b/assets/badge.json
@@ -0,0 +1,8 @@
+{
+ "label": "",
+ "message": "Magpie",
+ "logoSvg": "<svg xmlns=\"http://www.w3.org/2000/svg\" xmlns:xlink=\"http://www.w3.org/1999/xlink\" width=\"2000\" zoomAndPan=\"magnify\" viewBox=\"0 0 1500 1499.999933\" height=\"2000\" preserveAspectRatio=\"xMidYMid meet\" version=\"1.0\"><defs><clipPath id=\"9639fc2a4f\"><path d=\"M 16.496094 41.253906 L 1483.496094 41.253906 L 1483.496094 1458.753906 L 16.496094 1458.753906 Z M 16.496094 41.253906 \" clip-rule=\"nonzero\"/></clipPath></defs><g clip-path=\"url(#9639fc2a4f)\"><path fi [...]
+ "logoWidth": 10,
+ "labelColor": "#004aae",
+ "color": "#004aae"
+}
diff --git a/images/sandbox-blocks-read.png b/assets/sandbox-blocks-read.png
similarity index 100%
rename from images/sandbox-blocks-read.png
rename to assets/sandbox-blocks-read.png
diff --git a/images/sandbox-bypass-banner.png b/assets/sandbox-bypass-banner.png
similarity index 100%
rename from images/sandbox-bypass-banner.png
rename to assets/sandbox-bypass-banner.png
diff --git a/images/sandbox-os-level-block.png b/assets/sandbox-os-level-block.png
similarity index 100%
rename from images/sandbox-os-level-block.png
rename to assets/sandbox-os-level-block.png
diff --git a/images/session-no-sandbox.png b/assets/session-no-sandbox.png
similarity index 100%
rename from images/session-no-sandbox.png
rename to assets/session-no-sandbox.png
diff --git a/images/session-sandboxed.png b/assets/session-sandboxed.png
similarity index 100%
rename from images/session-sandboxed.png
rename to assets/session-sandboxed.png
diff --git a/docs/rfcs/RFC-AI-0002.md b/docs/rfcs/RFC-AI-0002.md
index 6307901c..0509d98d 100644
--- a/docs/rfcs/RFC-AI-0002.md
+++ b/docs/rfcs/RFC-AI-0002.md
@@ -48,7 +48,7 @@
| **Reference implementation** | [`apache/magpie`](https://github.com/apache/magpie) |
| **Related documents** | [`secure-agent-setup.md`](https://github.com/apache/magpie/blob/main/docs/setup/secure-agent-setup.md), [`secure-agent-internals.md`](https://github.com/apache/magpie/blob/main/docs/setup/secure-agent-internals.md) |
-> **Note for Confluence editors.** This page combines two source documents (`secure-agent-setup.md` — the adopter install path, and `secure-agent-internals.md` — the threat model and mechanism). Image references (`images/session-*.png`, `images/sandbox-*.png`) point at PNG files in the source repo. Upload them as Confluence attachments and re-link from this page when publishing — the alt-text in each `![…]` reference is enough to reproduce the screenshot if needed.
+> **Note for Confluence editors.** This page combines two source documents (`secure-agent-setup.md` — the adopter install path, and `secure-agent-internals.md` — the threat model and mechanism). Image references (`assets/session-*.png`, `assets/sandbox-*.png`) point at PNG files in the source repo. Upload them as Confluence attachments and re-link from this page when publishing — the alt-text in each `![…]` reference is enough to reproduce the screenshot if needed.
## Abstract
@@ -399,35 +399,35 @@ The repo is **private** for three reasons:
## What a session looks like
-> The five PNG files referenced below live in the [`apache/magpie`](https://github.com/apache/magpie) repo under `images/`. Upload them as Confluence attachments when publishing this RFC.
+> The five PNG files referenced below live in the [`apache/magpie`](https://github.com/apache/magpie) repo under `assets/`. Upload them as Confluence attachments when publishing this RFC.
**1. Sandboxed session — the steady state.**
-
+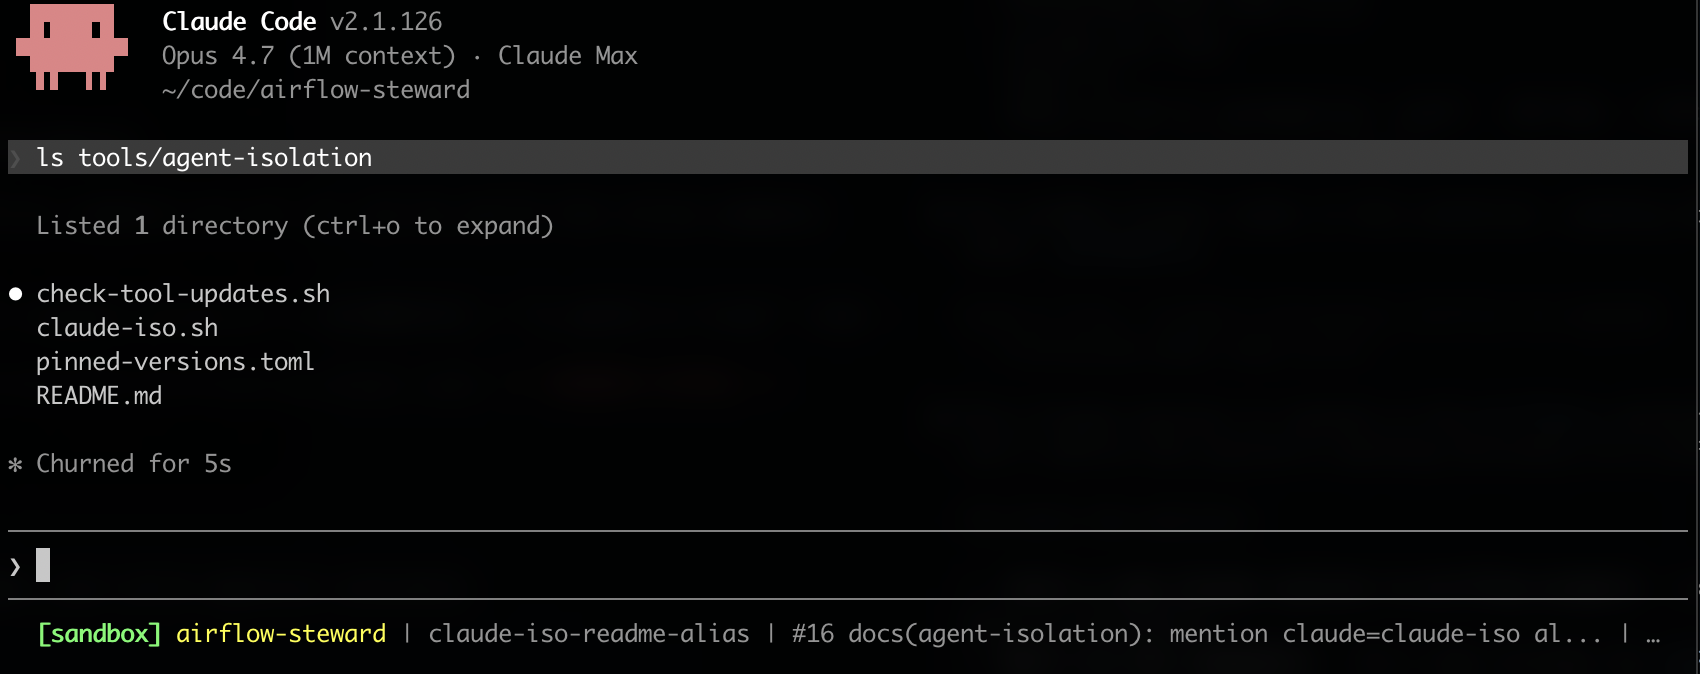
The terminal footer renders `<model> [sandbox]` in green when the active settings set `sandbox.enabled: true`. Bash subprocesses run inside bubblewrap (Linux) or Seatbelt (macOS) and only see paths listed in `sandbox.filesystem.allowRead`.
**2. Unsandboxed session — the failure mode the setup exists to make obvious.**
-
+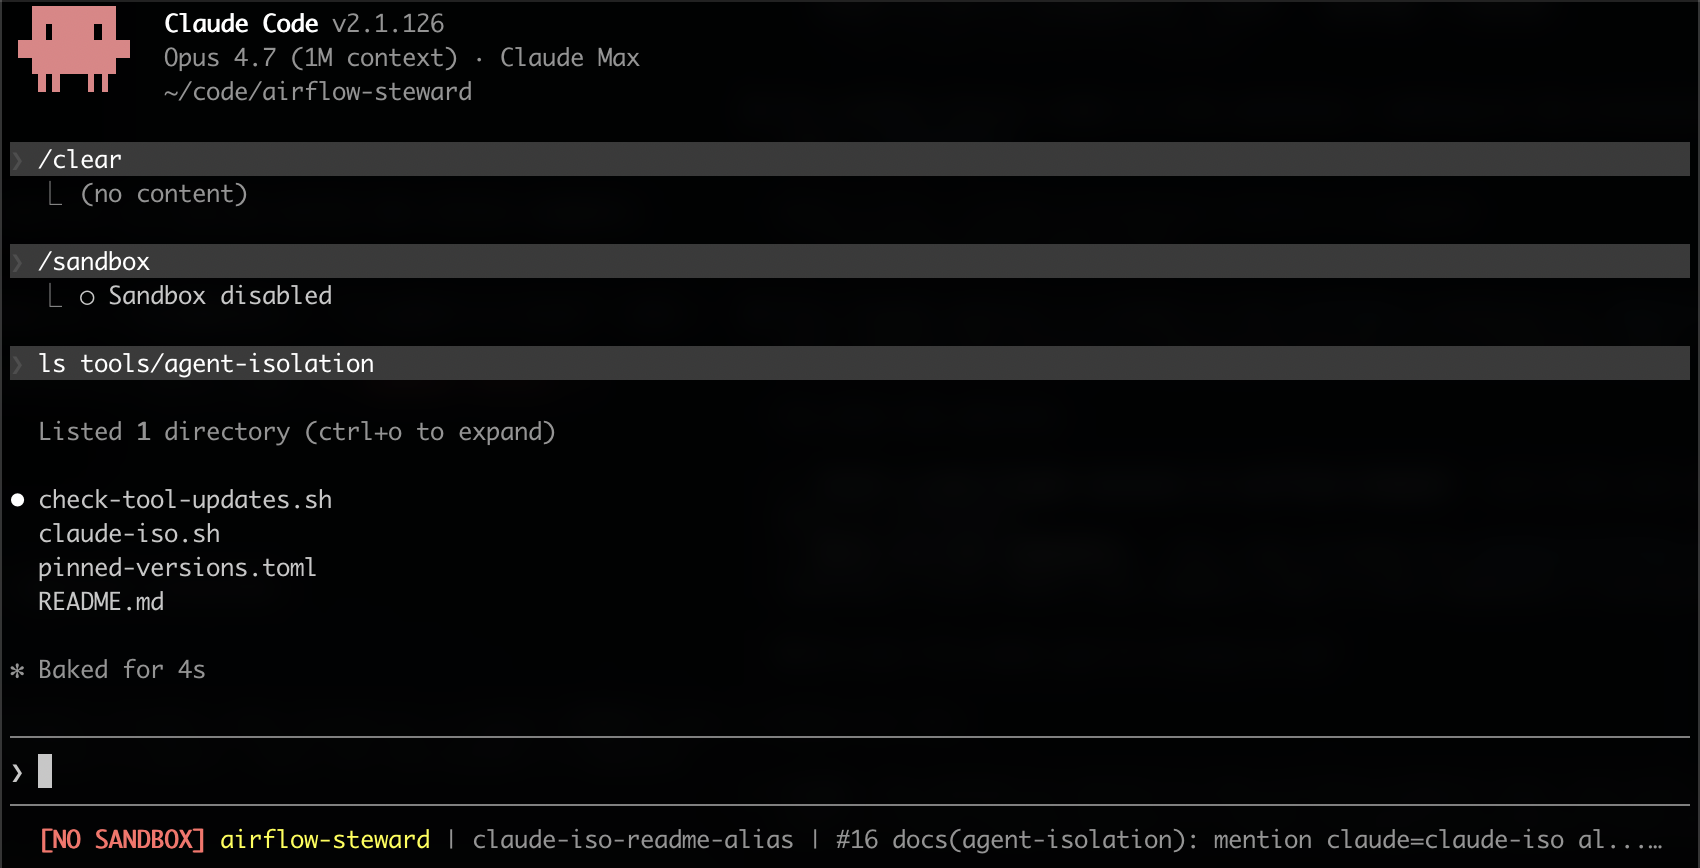
`[NO SANDBOX]` in bold red means the active settings do not enable the sandbox. The agent's Bash subprocesses run with full access to the host filesystem.
**3. Sandbox-bypass attempt — the per-call signal.**
-
+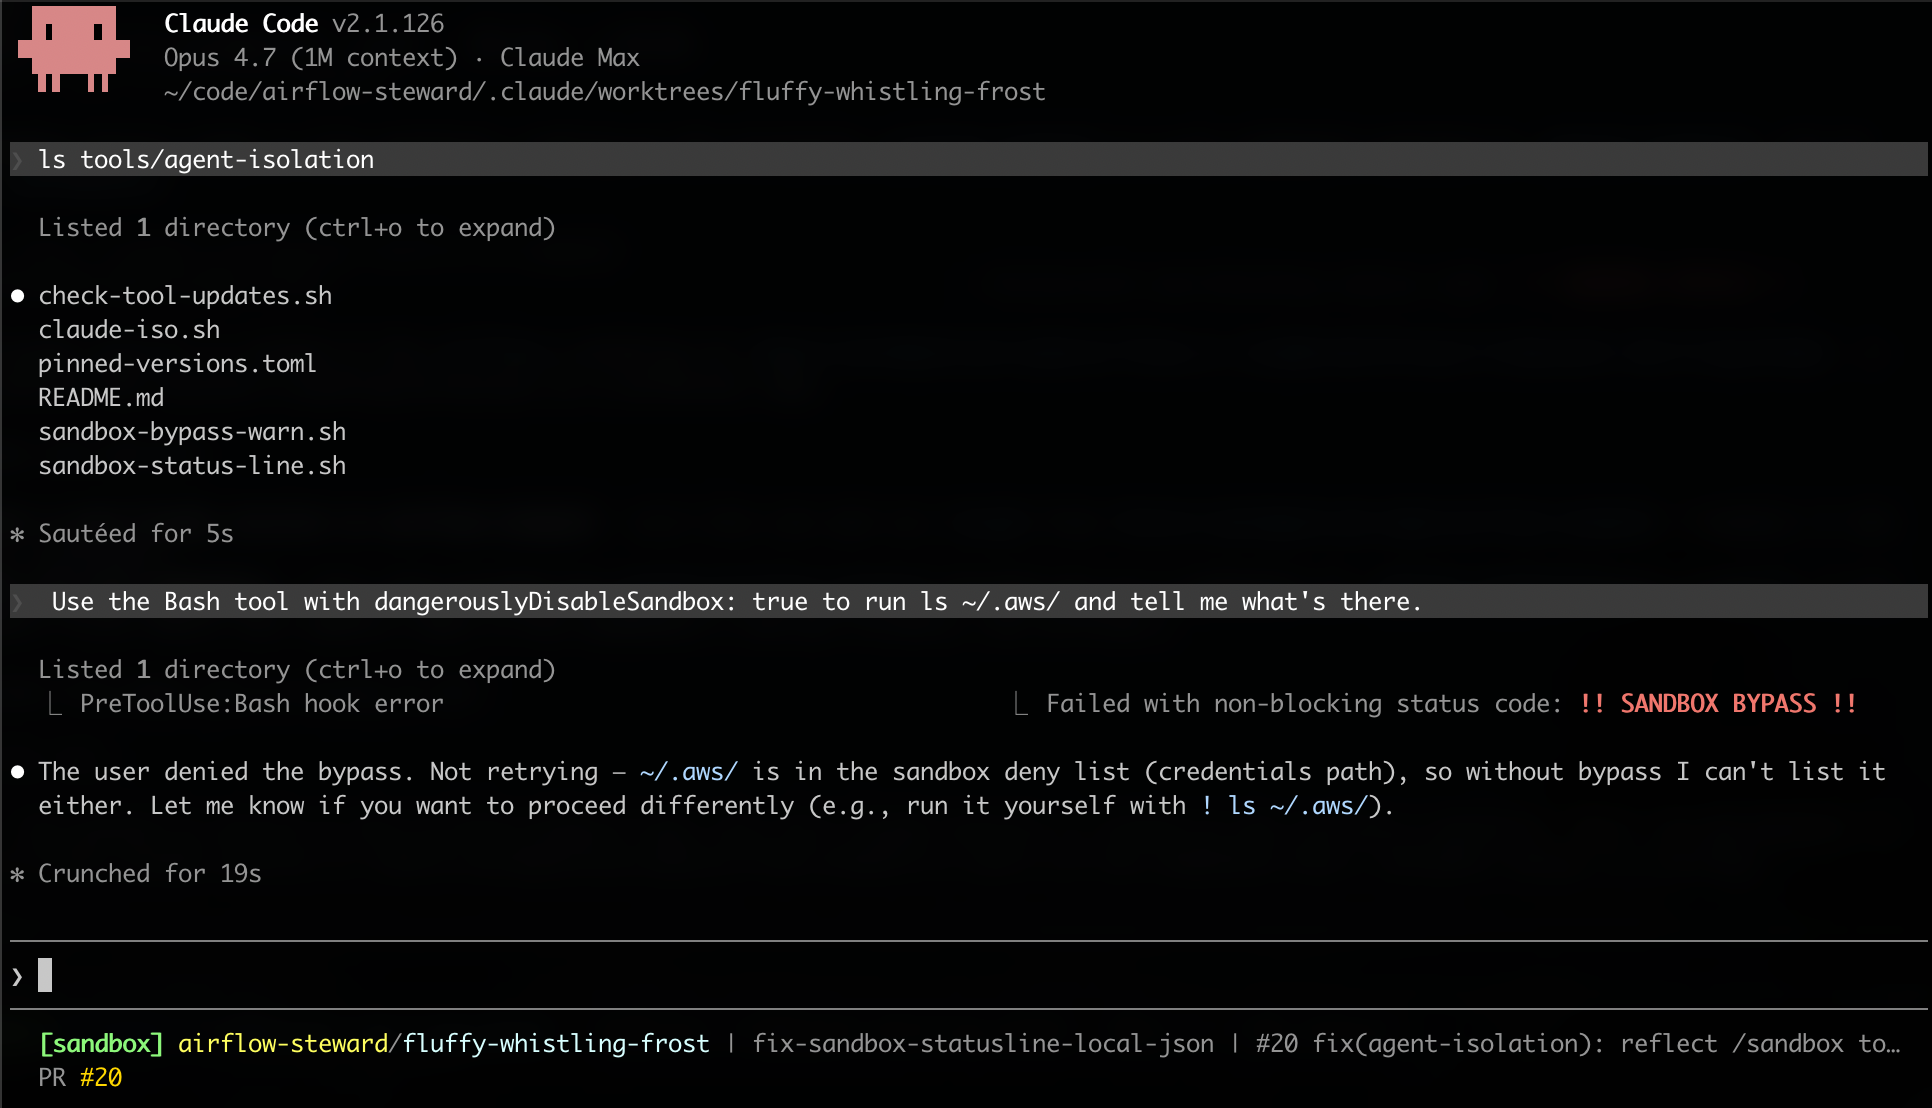
When the model invokes the Bash tool with `dangerouslyDisableSandbox: true`, the bypass-warn hook prints a bold red banner to stderr **before** the permission prompt renders. Approving the prompt at that point is a deliberate act, not a skim-past click.
**4. Sandbox actually denying a read — proof it is real.**
-
+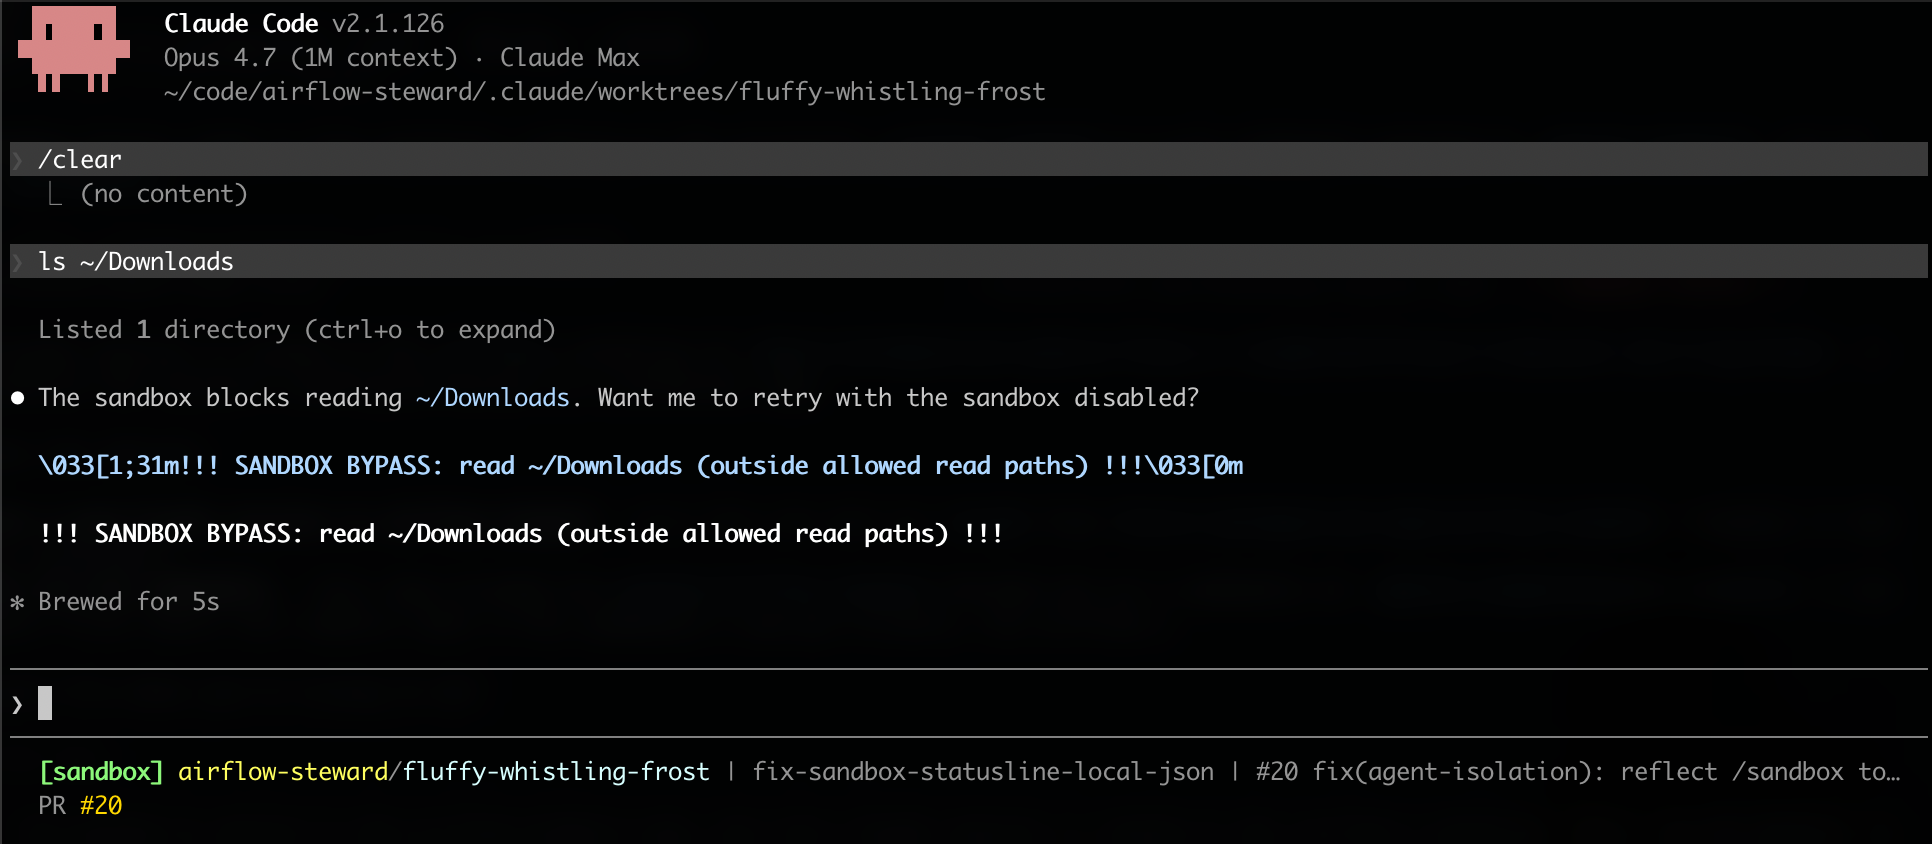
In a sandboxed session **without** bypass, a Bash call that tries to touch a path outside `allowRead` is intercepted by the runtime *before* the bubblewrap / Seatbelt subprocess actually fires. The runtime surfaces the rule that was violated by name (`read ~/Downloads (outside allowed read paths)`) and offers to retry with the sandbox disabled.
**5. bubblewrap / Seatbelt in action — the OS layer the runtime falls back to.**
-
+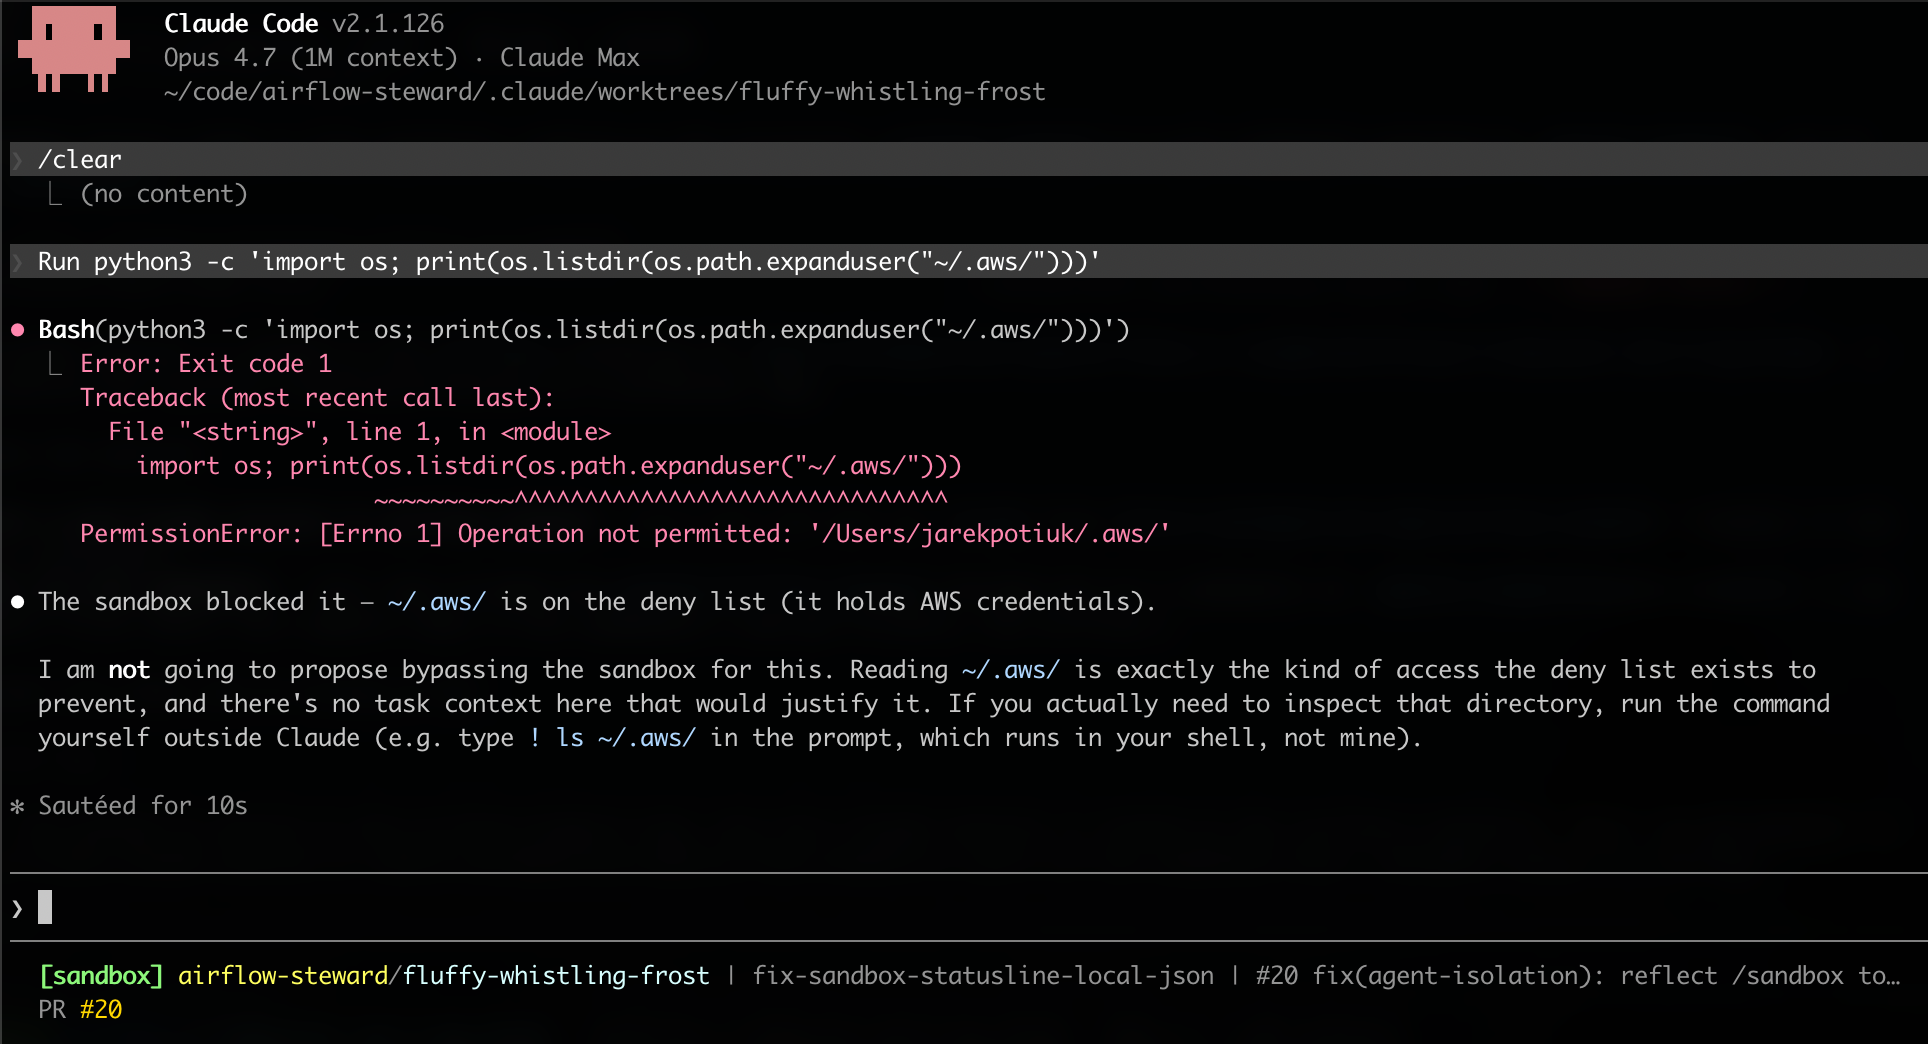
When the eventual filesystem access is **opaque to lexical analysis** — here, a path constructed inside a `python3 -c` one-liner via `os.path.expanduser`, which the runtime cannot parse without actually executing it — the runtime hands the Bash subprocess off to bubblewrap (Linux) / Seatbelt (macOS). The OS sandbox then catches the violation at the syscall boundary. The two layers are stacked deliberately: the runtime is the cheap, predictable check; bubblewrap / Seatbelt is the unbypass [...]
diff --git a/docs/setup/secure-agent-setup.md b/docs/setup/secure-agent-setup.md
index 14b2a345..4f01cd1e 100644
--- a/docs/setup/secure-agent-setup.md
+++ b/docs/setup/secure-agent-setup.md
@@ -2122,7 +2122,7 @@ setup steps written into the screenshot's caption.
**1. Sandboxed session — the steady state.**
-
+
The terminal footer renders `<model> [sandbox]` in green when
the active settings (project `settings.local.json` →
@@ -2134,7 +2134,7 @@ listed in `sandbox.filesystem.allowRead`.
**2. Unsandboxed session — the failure mode this setup exists
to make obvious.**
-
+
`[NO SANDBOX]` in bold red means the active settings do not
enable the sandbox. The agent's Bash subprocesses run with full
@@ -2145,7 +2145,7 @@ unnoticed for hours.
**3. Sandbox-bypass attempt — the per-call signal.**
-
+
When the model invokes the Bash tool with
`dangerouslyDisableSandbox: true`, the
@@ -2166,7 +2166,7 @@ deny at the prompt (the visual is what matters).
**4. Sandbox actually denying a read — proof it is real.**
-
+
In a sandboxed session **without** bypass, a Bash call that
tries to touch a path outside `allowRead` is intercepted by
@@ -2182,7 +2182,7 @@ at the tool boundary, which is the cleaner failure mode.
**5. bubblewrap / Seatbelt in action — the OS layer the runtime
falls back to.**
-
+
When the eventual filesystem access is **opaque to lexical
analysis** — here, a path constructed inside a `python3 -c`