You are viewing a plain text version of this content. The canonical link for it is here.
Posted to issues@solr.apache.org by GitBox <gi...@apache.org> on 2022/12/14 16:47:28 UTC
[GitHub] [solr-site] raboof opened a new pull request, #86: First draft presenting dependency vulnerability info
raboof opened a new pull request, #86:
URL: https://github.com/apache/solr-site/pull/86

   To replace https://cwiki.apache.org/confluence/display/SOLR/SolrSecurity#SolrSecurity-SolrandVulnerabilityScanningTools and ask for collaboration and experiences on approaches to VEX as discussed in https://lists.apache.org/thread/j35clzm48s7xxc9671qogzr54bsdj1lz


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy merged pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy merged PR #86:
URL: https://github.com/apache/solr-site/pull/86


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380679746

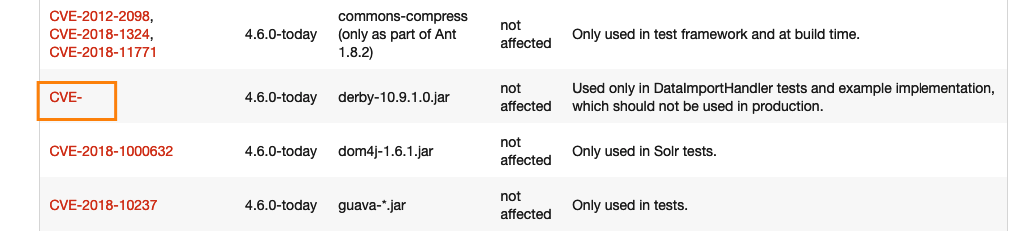
   @epugh that missing CVE is lacking also on the wiki page. I tried a quick cve search for derby-10.9.1.0.jar but could not find a number for it either...


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] risdenk commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
risdenk commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049844493


##########
requirements.txt:
##########
@@ -5,6 +5,9 @@ checksumdir~=1.2.0
 # Pelican plugins
 mdx-include~=1.4.1
 beautifulsoup4~=4.9.3
+# Dependencies of the vex plugin
+jsonschema
+jsonref

Review Comment:
   These should have version numbers specified like other dependencies.


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049069644


##########
content/pages/security.md:
##########
@@ -10,17 +10,42 @@ Every CVE that is detected by a software scanner is by definition already public

 To find a path forward in addressing a detected CVE we suggest the following process for fastest results:

-1. Check further down this page to see if the CVE is listed as exploitable in Solr.
-2. Check the [officially published non-exploitable vulnerabilities](https://cwiki.apache.org/confluence/display/SOLR/SolrSecurity#SolrSecurity-SolrandVulnerabilityScanningTools) list to see if the CVE is listed as not exploitable in Solr.
+1. Check [further down this page](#recent-cve-reports-for-apache-solr) to see if the CVE is listed as exploitable in Solr.
+2. Check the [officially published non-exploitable vulnerabilities](#cve-reports-for-apache-solr-dependencies) list to see if the CVE is listed as not exploitable in Solr.
 3. Search through the [Solr users mailing list archive](https://lists.apache.org/list.html?users@solr.apache.org)  to see if anyone else has brought up this dependency CVE.
 4. If no one has, then please do [subscribe to the users mailing list](https://solr.apache.org/community.html#mailing-lists-chat) and then send an email asking about the CVE.

+#### VEX
+Since the process of checking whether CVEs in dependencies of Solr affect your

Review Comment:
   I'd prefer if the "VEX" chapter was pushed to the bottom of the page, next to the new table?

   As it stands now, it takes up much real-estate, and I think we generally should be more to the point. As it is now we tend to grow the "intro" part of the security page on every edit, so users have to read tons of text before they get to the "meat".


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] raboof commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
raboof commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049644651


##########
vex-input.json:
##########
@@ -0,0 +1,468 @@
+[
+  {
+    "ids": [
+      "CVE-2022-33980"
+    ],
+    "versions": "< 9.1",
+    "jars": [
+      "commons-configuration2-2.7.jar"
+    ],
+    "analysis": {
+      "state": "not_affected",
+      "detail": "Solr uses commons-configuration2 for \"hadoop-auth\" only (for Kerberos). It is only used for loading Hadoop configuration files that would only ever be provided by trusted administrators, not externally (untrusted)."
+    }
+  },

Review Comment:
   Added schema validation both for the input and the output


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049070224


##########
content/pages/security.md:
##########
@@ -10,17 +10,42 @@ Every CVE that is detected by a software scanner is by definition already public

 To find a path forward in addressing a detected CVE we suggest the following process for fastest results:

-1. Check further down this page to see if the CVE is listed as exploitable in Solr.
-2. Check the [officially published non-exploitable vulnerabilities](https://cwiki.apache.org/confluence/display/SOLR/SolrSecurity#SolrSecurity-SolrandVulnerabilityScanningTools) list to see if the CVE is listed as not exploitable in Solr.
+1. Check [further down this page](#recent-cve-reports-for-apache-solr) to see if the CVE is listed as exploitable in Solr.
+2. Check the [officially published non-exploitable vulnerabilities](#cve-reports-for-apache-solr-dependencies) list to see if the CVE is listed as not exploitable in Solr.
 3. Search through the [Solr users mailing list archive](https://lists.apache.org/list.html?users@solr.apache.org)  to see if anyone else has brought up this dependency CVE.
 4. If no one has, then please do [subscribe to the users mailing list](https://solr.apache.org/community.html#mailing-lists-chat) and then send an email asking about the CVE.

+#### VEX
+Since the process of checking whether CVEs in dependencies of Solr affect your
+Solr deployment is tedious and error-prone, we are experimenting with sharing
+information about advisories that are known (not) to affect Solr in a
+machine-readable way.
+
+File formats to share this information are called 'VEX' formats. A number of
+such formats are under active development, such as based on
+[CycloneDX](https://cyclonedx.org/capabilities/vex/) and
+[CSAF](https://github.com/oasis-tcs/csaf/blob/master/csaf_2.0/prose/csaf-v2-editor-draft.md#45-profile-5-vex).
+
+We are currently providing vulnerability information in a CycloneDX JSON-based
+format [here](/solr.vex.json). We are very curious to hear about your experience,
+and to find out what is still missing to reduce the signal/noise ratio and make
+these tools more effective. We invite you to join the discussion at the
+[security-discuss](mailto:security-discuss@community.apache.org)
+[mailinglist](https://www.apache.org/foundation/mailinglists.html) or,
+if you prefer to collaborate in private, contact
+[security@apache.org](mailto:security@apache.org). It will likely be interesting
+to know what security scanning/reporting tool you are using, exactly on which
+artifacts, and if/how its vendor appears to support VEX. We'd be happy to work
+with you to see if we can provide this information in other variations or formats.
+
 #### Dos and Don'ts
 * Please DO discuss the possible need for library upgrades on the user list.
 * Please DO search Jira for the CVE number to see if we are addressing it already.
 * Please DO create Jira issues and associated pull requests to propose and discuss upgrades of *a single specific* dependency.
 * Please DO NOT attach a scan report, or paste output of a scan into Jira (just link the CVE instead)
 * Please DO NOT email the security email below with a scan report it will be ignored.
+* Please DO talk to your scanning tool vendor about supporting VEX.
+* Please DO share your experience with incorporating VEX into your toolchain on the [security-discuss@community.apache.org](mailto:security-discuss@community.apache.org) [mailinglist](https://www.apache.org/foundation/mailinglists.html) or with [security@apache.org](mailto:security@apache.org).

Review Comment:
   Also, two extra bullet points about technicality of VEX format seems overkill. The first one could perhaps stay, but the other line with a call for feedback could be embedded in the "VEX" chapter furher down the page.


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] epugh commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
epugh commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380588153
--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For queries about this service, please contact Infrastructure at:
users@infra.apache.org
---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049069644


##########
content/pages/security.md:
##########
@@ -10,17 +10,42 @@ Every CVE that is detected by a software scanner is by definition already public

 To find a path forward in addressing a detected CVE we suggest the following process for fastest results:

-1. Check further down this page to see if the CVE is listed as exploitable in Solr.
-2. Check the [officially published non-exploitable vulnerabilities](https://cwiki.apache.org/confluence/display/SOLR/SolrSecurity#SolrSecurity-SolrandVulnerabilityScanningTools) list to see if the CVE is listed as not exploitable in Solr.
+1. Check [further down this page](#recent-cve-reports-for-apache-solr) to see if the CVE is listed as exploitable in Solr.
+2. Check the [officially published non-exploitable vulnerabilities](#cve-reports-for-apache-solr-dependencies) list to see if the CVE is listed as not exploitable in Solr.
 3. Search through the [Solr users mailing list archive](https://lists.apache.org/list.html?users@solr.apache.org)  to see if anyone else has brought up this dependency CVE.
 4. If no one has, then please do [subscribe to the users mailing list](https://solr.apache.org/community.html#mailing-lists-chat) and then send an email asking about the CVE.

+#### VEX
+Since the process of checking whether CVEs in dependencies of Solr affect your

Review Comment:
   I'd prefer if the "VEX" chapter was pushed to the bottom of the page, next to the new table, it takes up much real-estate and I think we should be more to the point. As it is now we continue to grow the "intro" part of security page so users have to read tons of text before they get to the "meat".


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049073745


##########
vex-input.json:
##########
@@ -0,0 +1,468 @@
+[
+  {
+    "ids": [
+      "CVE-2022-33980"
+    ],
+    "versions": "< 9.1",
+    "jars": [
+      "commons-configuration2-2.7.jar"
+    ],
+    "analysis": {
+      "state": "not_affected",
+      "detail": "Solr uses commons-configuration2 for \"hadoop-auth\" only (for Kerberos). It is only used for loading Hadoop configuration files that would only ever be provided by trusted administrators, not externally (untrusted)."
+    }
+  },

Review Comment:
   Can we use some tooling/editor or at least a linter when adding entries to this json file, so we're sure it is parsable? Will probably get a Pelican build failure if something is wrong?


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380504219

   > Not sure it makes sense to integrate those exclusions here as well - but something to keep in mind.

   Would be nice if we could maintain one vex file that could be used both at this website as well as to mute false positives in owasp.

   And I guess the idea is that anyone could download our vex file, and use it to "tame" the output of their own scanners so they get a much smaller output that is not yet vetted..


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380606828

   I'm stuck on this, here is ASF docs on pelican builder https://infra.apache.org/asf-pelican-build.html


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380597980

   Here is the log of apache buildbot https://ci2.apache.org/#/builders/3/builds/19190/steps/1/logs/stdio

   Look at the last lines there:
   ```
   Building web site with: ('/bin/bash', '-c', 'source bin/activate; cd source && (pelican content  -o /tmp/solr/build/output)')
   20 html files.
   Web site successfully generated!
   Copying web site to branch: asf-staging
   - Doing fresh checkout of branch asf-staging
   - Adding new content to branch
   Removing existing output dir /tmp/solr/source/output
   - Committing and pushing to https://gitbox.apache.org/repos/asf/solr-site.git
   Web site generated and published successfully!
   ```

   So it appears to me that pelican has some explicit knowledge of what files is updated, and in "Adding new content to branch" it fails to copy `solr.vex.json` which was output "under the radar"?.


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380655936

   @raboof found the issue when chatting with asfinfra, the asf buildbot specifies a custom output directory, but the plugin writes the json file to local `output/`. Likely to be fixed in a new PR.


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] raboof commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
raboof commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049644130


##########
content/pages/security.md:
##########
@@ -10,17 +10,42 @@ Every CVE that is detected by a software scanner is by definition already public

 To find a path forward in addressing a detected CVE we suggest the following process for fastest results:

-1. Check further down this page to see if the CVE is listed as exploitable in Solr.
-2. Check the [officially published non-exploitable vulnerabilities](https://cwiki.apache.org/confluence/display/SOLR/SolrSecurity#SolrSecurity-SolrandVulnerabilityScanningTools) list to see if the CVE is listed as not exploitable in Solr.
+1. Check [further down this page](#recent-cve-reports-for-apache-solr) to see if the CVE is listed as exploitable in Solr.
+2. Check the [officially published non-exploitable vulnerabilities](#cve-reports-for-apache-solr-dependencies) list to see if the CVE is listed as not exploitable in Solr.
 3. Search through the [Solr users mailing list archive](https://lists.apache.org/list.html?users@solr.apache.org)  to see if anyone else has brought up this dependency CVE.
 4. If no one has, then please do [subscribe to the users mailing list](https://solr.apache.org/community.html#mailing-lists-chat) and then send an email asking about the CVE.

+#### VEX
+Since the process of checking whether CVEs in dependencies of Solr affect your
+Solr deployment is tedious and error-prone, we are experimenting with sharing
+information about advisories that are known (not) to affect Solr in a
+machine-readable way.
+
+File formats to share this information are called 'VEX' formats. A number of
+such formats are under active development, such as based on
+[CycloneDX](https://cyclonedx.org/capabilities/vex/) and
+[CSAF](https://github.com/oasis-tcs/csaf/blob/master/csaf_2.0/prose/csaf-v2-editor-draft.md#45-profile-5-vex).
+
+We are currently providing vulnerability information in a CycloneDX JSON-based
+format [here](/solr.vex.json). We are very curious to hear about your experience,
+and to find out what is still missing to reduce the signal/noise ratio and make
+these tools more effective. We invite you to join the discussion at the
+[security-discuss](mailto:security-discuss@community.apache.org)
+[mailinglist](https://www.apache.org/foundation/mailinglists.html) or,
+if you prefer to collaborate in private, contact
+[security@apache.org](mailto:security@apache.org). It will likely be interesting
+to know what security scanning/reporting tool you are using, exactly on which
+artifacts, and if/how its vendor appears to support VEX. We'd be happy to work
+with you to see if we can provide this information in other variations or formats.
+
 #### Dos and Don'ts
 * Please DO discuss the possible need for library upgrades on the user list.
 * Please DO search Jira for the CVE number to see if we are addressing it already.
 * Please DO create Jira issues and associated pull requests to propose and discuss upgrades of *a single specific* dependency.
 * Please DO NOT attach a scan report, or paste output of a scan into Jira (just link the CVE instead)
 * Please DO NOT email the security email below with a scan report it will be ignored.
+* Please DO talk to your scanning tool vendor about supporting VEX.
+* Please DO share your experience with incorporating VEX into your toolchain on the [security-discuss@community.apache.org](mailto:security-discuss@community.apache.org) [mailinglist](https://www.apache.org/foundation/mailinglists.html) or with [security@apache.org](mailto:security@apache.org).

Review Comment:
   :+1: condensed it into one bullet referring to the chapter


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] raboof commented on a diff in pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
raboof commented on code in PR #86:
URL: https://github.com/apache/solr-site/pull/86#discussion_r1049643505


##########
content/pages/security.md:
##########
@@ -10,17 +10,42 @@ Every CVE that is detected by a software scanner is by definition already public

 To find a path forward in addressing a detected CVE we suggest the following process for fastest results:

-1. Check further down this page to see if the CVE is listed as exploitable in Solr.
-2. Check the [officially published non-exploitable vulnerabilities](https://cwiki.apache.org/confluence/display/SOLR/SolrSecurity#SolrSecurity-SolrandVulnerabilityScanningTools) list to see if the CVE is listed as not exploitable in Solr.
+1. Check [further down this page](#recent-cve-reports-for-apache-solr) to see if the CVE is listed as exploitable in Solr.
+2. Check the [officially published non-exploitable vulnerabilities](#cve-reports-for-apache-solr-dependencies) list to see if the CVE is listed as not exploitable in Solr.
 3. Search through the [Solr users mailing list archive](https://lists.apache.org/list.html?users@solr.apache.org)  to see if anyone else has brought up this dependency CVE.
 4. If no one has, then please do [subscribe to the users mailing list](https://solr.apache.org/community.html#mailing-lists-chat) and then send an email asking about the CVE.

+#### VEX
+Since the process of checking whether CVEs in dependencies of Solr affect your

Review Comment:
   I moved it down to near the end of the markdown content of the page. That's still above the existing table, because the tables are generated as part as the HTML template, and it doesn't seem easy to intersperse markdown and HTML content.

   I'm also OK with moving it further down, but AFAICS that'd mean we'd have to include it in the HTML template instead of having it as Markdown - not sure if that's worth it?


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: First draft presenting dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1352356257

   Thanks for this. Looks great - see screenshots.

   <img width="990" alt="Skjermbilde 2022-12-15 kl  00 19 01" src="https://user-images.githubusercontent.com/409128/207736218-d30f5883-d385-4a47-802d-ca165259bd65.png">

   <img width="1005" alt="Skjermbilde 2022-12-15 kl  00 19 26" src="https://user-images.githubusercontent.com/409128/207736232-60bdae3a-76ad-4e97-80e1-5e2b675f9e32.png">

   @dsmiley you wished for a page that was crawlable/searchable, and this, being statically generated by Pelican, should satisfy that.


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380580846

   I can see that `solr.vex.json` is copied to `output/` folder and works locally. But it is not present in the output folder generated by ASF builder here https://github.com/apache/solr-site/tree/asf-staging/output


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] HoustonPutman commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
HoustonPutman commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380641483

   So would it be possible to:

   1. add another gitignore directory
   2. have the plugin output the vex file to this directory
   3. add this directory to `STATIC_PATHS`

   That way we are giving pelican the files in the way that it wants.


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] raboof commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
raboof commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380681227

   > @epugh that missing CVE is lacking also on the wiki page. I tried a quick cve search for derby-10.9.1.0.jar but could not find a number for it either...

   yeah, weird - I'll PR to remove the entry for now


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org
[GitHub] [solr-site] janhoy commented on pull request #86: Share dependency vulnerability info
Posted by GitBox <gi...@apache.org>.
janhoy commented on PR #86:
URL: https://github.com/apache/solr-site/pull/86#issuecomment-1380526769

   The staged page is now viewable at https://solr.staged.apache.org/security.html

   Looks good, but the supposed link to /solr.vex.json (https://solr.staged.apache.org/solr.vex.json) does not work. Have not looked into it, do you think you can fix @raboof ?


--
This is an automated message from the Apache Git Service.
To respond to the message, please log on to GitHub and use the
URL above to go to the specific comment.

To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org

For queries about this service, please contact Infrastructure at:
users@infra.apache.org


---------------------------------------------------------------------
To unsubscribe, e-mail: issues-unsubscribe@solr.apache.org
For additional commands, e-mail: issues-help@solr.apache.org