You are viewing a plain text version of this content. The canonical link for it is here.
Posted to notifications@apisix.apache.org by ju...@apache.org on 2022/07/06 07:57:44 UTC
[apisix-website] branch doc-keycloak updated: docs: added how to use keycloak with api gateway?
This is an automated email from the ASF dual-hosted git repository.
juzhiyuan pushed a commit to branch doc-keycloak
in repository https://gitbox.apache.org/repos/asf/apisix-website.git
The following commit(s) were added to refs/heads/doc-keycloak by this push:
new 281087c7fc1 docs: added how to use keycloak with api gateway?
281087c7fc1 is described below
commit 281087c7fc14cef8bb211b0d596c317f5c5f419b
Author: juzhiyuan <ju...@apache.org>
AuthorDate: Wed Jul 6 15:57:29 2022 +0800
docs: added how to use keycloak with api gateway?
---
website/blog/2022/07/06/how-to-use-keycloak-with-api-gateway.md | 6 +++++-
1 file changed, 5 insertions(+), 1 deletion(-)
diff --git a/website/blog/2022/07/06/how-to-use-keycloak-with-api-gateway.md b/website/blog/2022/07/06/how-to-use-keycloak-with-api-gateway.md
index 81bc06eb46b..729850e0f19 100644
--- a/website/blog/2022/07/06/how-to-use-keycloak-with-api-gateway.md
+++ b/website/blog/2022/07/06/how-to-use-keycloak-with-api-gateway.md
@@ -11,10 +11,14 @@ keywords:
- Authentication
- OpenID Connect
- Keycloak
-description:
+description: This article describes how API Gateway integrates with Keycloak (OpenID Connect Provider) to secure your APIs.
tags: [Authentication]
---
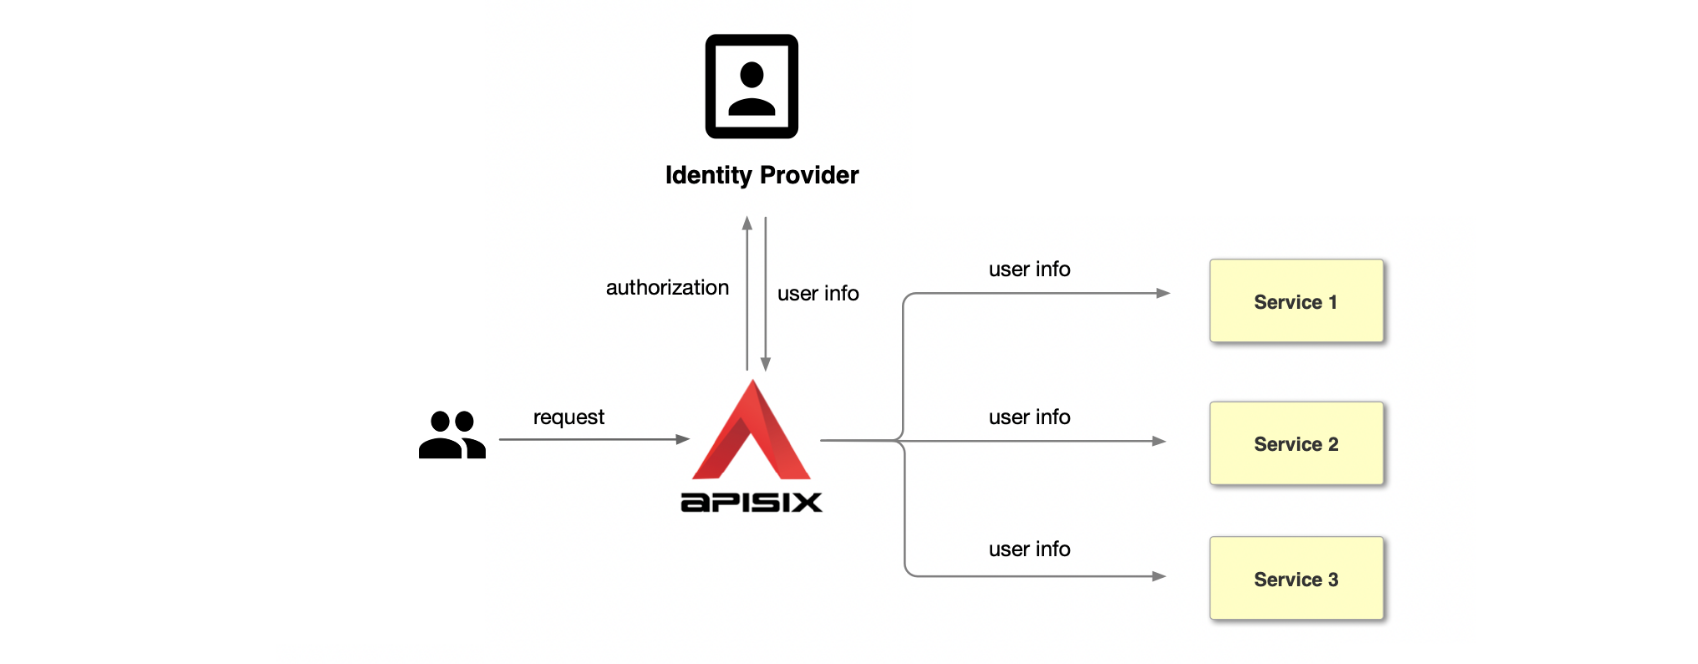
+> This article describes how Apache APISIX integrates with Keycloak (OpenID Connect Provider) to secure your APIs.
+
+<!--truncate-->
+
OpenID Connect referred to as OIDC, is an authentication protocol based on the OAuth 2.0. It allows the client to obtain user information from the identity provider (IdP), e.g., Keycloak, Ory, Okta, Auth0, etc. The open-source API Gateway Apache APISIX supports using the [openid-connect plugin](https://apisix.apache.org/docs/apisix/plugins/openid-connect) to integrate with the above Identify Providers. It will redirect all unauthenticated clients to IdP's login page. After the successful [...]